Export Your Splunk Cloud Apps
Splunk Cloud Platform recently got an exciting new feature, it’s the new app export feature which provides cloud admins self-service capability to export app configuration files and associated app data.
Read more
Splunk Cloud Platform recently got an exciting new feature, it’s the new app export feature which provides cloud admins self-service capability to export app configuration files and associated app data.
Read more
We had a recent request to create a Splunk alert that runs hourly with a time range of midnight UTC of current date to current time. This sounds like an easy request, but when you look into it it’s a bit more complicated than it seems.
Read more
Integrating Splunk Enterprise Security (ES) with Splunk Security Orchestration, Automation and Response (SOAR) can significantly enhance your organization’s security operations. By automating alert handling and response processes, this integration streamlines security incident management and enables faster, more effective threat mitigation. Splunk SOAR empowers security teams to automate actions based on Splunk ES detections using assigned playbooks, enabling seamless incident resolution.
Read more

Have you ever wished you had a fresh ephemeral Splunk instance that you could quickly spin up, run some tests and then kill it, with maximum speed and minimum cloud costs?
Enter Hashi Terraform to the rescue. The industry-leading infrastructure-as-code tool makes the standup, setup and teardown of cloud compute nodes simple, speedy and repeatable so that an environment can be built, a complete set of tests can be run, results received and the test nodes destroyed in minutes rather than hours.
In this whitepaper, I show how I set up my computer and built the Search Head and Deployment server, as well as how I set up the many Splunk Universal Forwarders to satisfy the test plan.
Get access to this exciting whitepaper now, by completing the form below.
Still winding down from the incredible experience at .conf24, where we delved into the latest market trends, we’ve uncovered several fascinating enhancements for the Splunk platform. These improvements not only elevate the performance and efficiency of Splunk but also offer exciting features that will be available in future releases. Join us as we explore four powerful upgrades that can be used in your Splunk environment.
Read more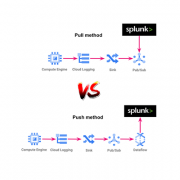
By: Carlos Moreno Buitrago and Anoop Ramachandran
In this blog we will talk about the processes and the options we have to collect the GCP events and we will see how to collect those in Splunk. In addition, we will even add integration with Cribl, as an optional step, in order to facilitate and optimize the process of information ingestion. After synthesizing all of this great information, you will have a great understanding of the available options to take, depending on the conditions of the project or team in which you work.
Read moreAs of Splunk 6.2, there is a Key-Value (KV) store baked into the Splunk Search Head. The Splunk KV store leverages MongoDB under the covers and among other things, can be leveraged for lookups and state tables. Better yet, unlike regular Splunk CSV lookups, you can actually update individual rows in the lookup without rebuilding the entire lookup – pretty cool! In this article, we will show you a quick way of how you can leverage the KV store as a lookup or state table. Read more
The following blog posting provides guidance on steps that can be taken to secure and harden Splunk environments. Many of the security feature essentially follow security best practices, while others would probably only be implemented if there was a business or regulatory need to do so. Read more
So many people talk about the need to index tweets from twitter into Splunk, that I figured I would write a post to explain just how easy it is. Within 10 steps and a few minutes, you will be streaming real-time tweets into Splunk, with the fields all extracted and the twitter data fully searchable. Read more