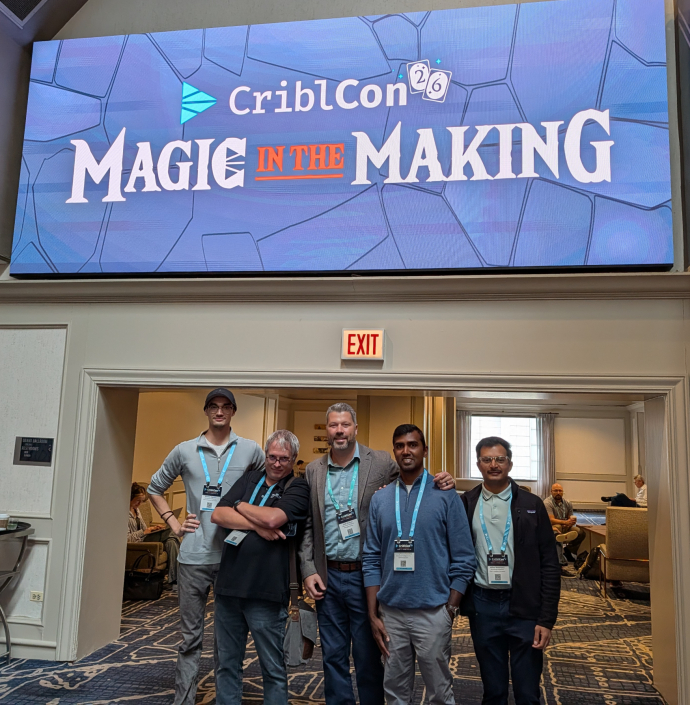
Key Takeaways from CriblCon 2026
Last week, our team had the opportunity to travel to Chicago…
Tips For Diving Into The New Cribl App Development Framework
Traditionally, we have had to solve complex data or security…
Config Quest for Cribl: App Demo
Managing distributed data pipelines can quickly feel like searching…
Boosting Sec Ops Efficiency: A Practical Guide to the Splunk AI Toolkit
If you are running a modern SOC or managing complex infrastructure,…
Introducing Config Quest for Cribl: The All-in-One App for Configuration Visibility and Hygiene
If you’ve spent any time running Cribl Stream across large,…
The New Reality of AI Risk & Governance
Summer is shaping up to be a critical period. Four things are converging:
Assessing What Matters with a Data Assessment Workshop
As organizations rush to deploy next-generation technologies,…
Introducing the Update Cribl Lookup App for Splunk
We’re excited to announce the public availability of our Update…
Introducing the Cribl Search App for Splunk
We’re excited to announce the public availability of our…
Ditch the Deployment Server: Why We Used Ansible for Splunk in a Secure OT Environment
Have you ever tried to manage a net-new Splunk deployment across…
Splunk Universal Forwarder Upgrades: From Manual Pain to Automated Gain
When was the last time you actually looked forward to upgrading…
Migrating Syslog to Cribl Stream: The Art of the “Zero Change” Migration
We’ve all been there. You’re ready to modernize your observability…
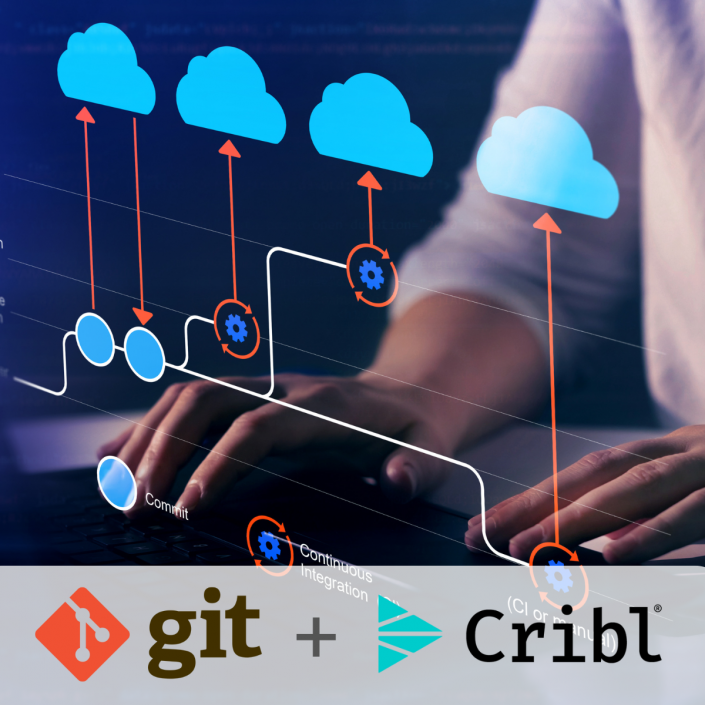
Cribl and GitOps: From Development to Production
If you’re running Cribl Stream in a distributed environment,…
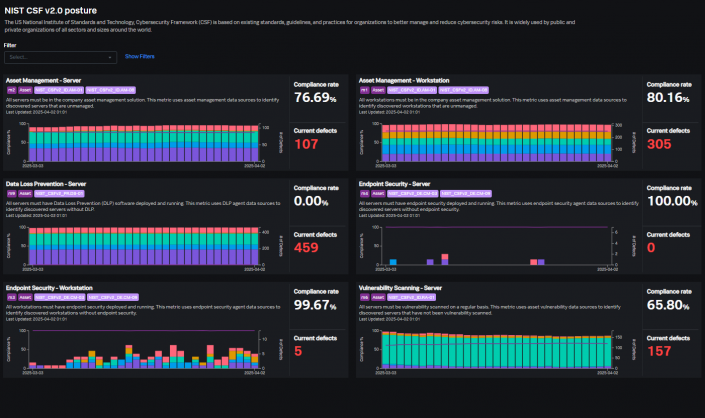
Finding Asset and Identity Risk with Splunk Asset and Risk Intelligence
Splunk Asset and Risk Intelligence (Splunk ARI) discovers and…
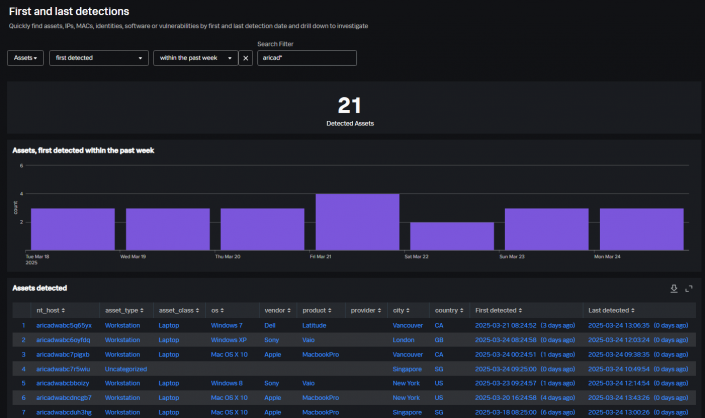
Reveal Asset and Identity Activity with Splunk Asset and Risk Intelligence
Splunk Asset and Risk Intelligence (Splunk ARI) keeps track…
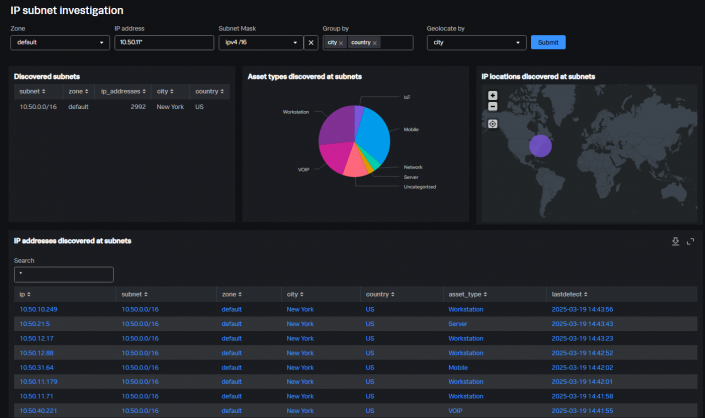
Investigating Assets and Identities with Splunk Asset and Risk Intelligence
Splunk Asset and Risk Intelligence (Splunk ARI) has powerful…
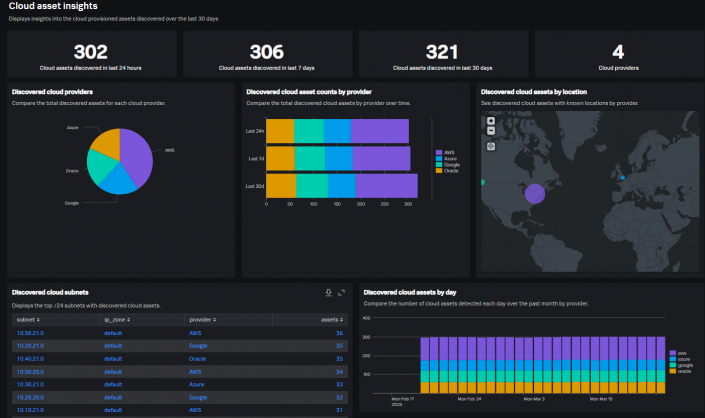
Discovering Assets and Identities with Splunk Asset and Risk Intelligence
Splunk Asset and Risk Intelligence (Splunk ARI) continually…

Field Filters 101: The Basics You Need to Know
Field filters (FF) provide a flexible way to control access to sensitive data at search time by redacting, replacing, or obfuscating sensitive fields in search results